
Important internal communication is spread across tools with different ownership and operating assumptions.
SYNCPAD / ORGANIZATIONAL COMMUNICATION
Communication becomes an infrastructure decision
when control starts to matter.
SyncPad is evaluated as a NetWelop product for controlled organizational communication. The conversation starts with the organization’s control requirements, operating environment and technical boundaries—not with a generic chat feature list.
WHY CONTROL MAY MATTER
The problem is not always messaging.
Sometimes it is the environment around it.
SyncPad is worth evaluating when organizational context, control and deployment questions matter alongside the communication itself.
Messages and files do not always live inside the same organizational context.
Administration, access and infrastructure responsibility need to be clearer than a consumer app can provide.
The real requirement is broader than a list of chat features and needs technical evaluation.
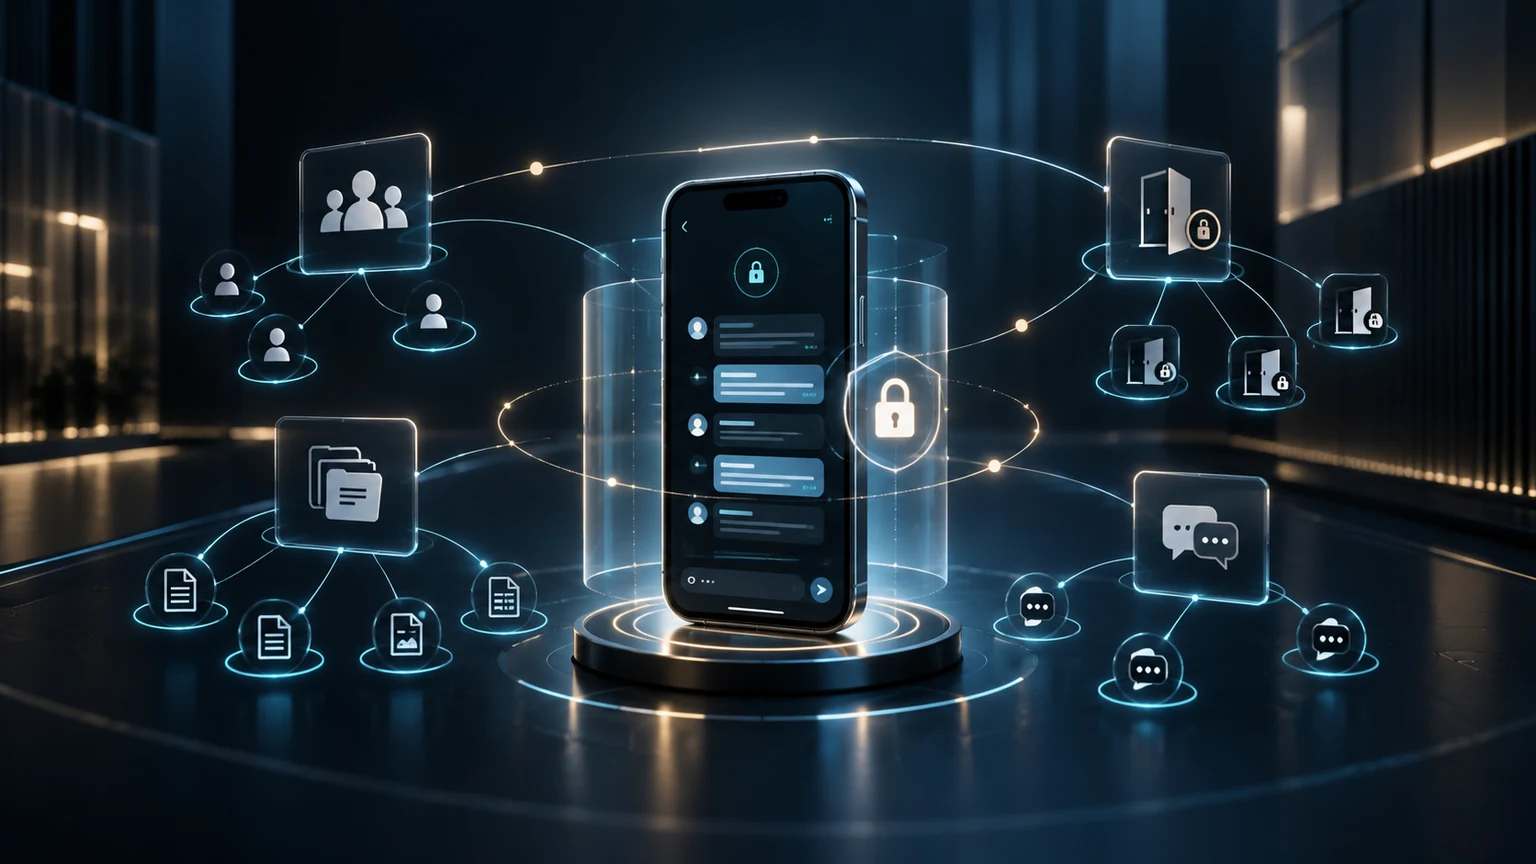
CONTROL ENVELOPE / CONCEPTUAL MODEL
Keep communication inside
a clearer organizational context.
The model below is deliberately conceptual. A real deployment is evaluated against the verified technical architecture, administration model and the organization’s actual constraints.
people files organizational boundary
SYNCPADORGANIZATIONAL
CONTEXT
CONTEXT
TEAM
COLLEAGUE
FILES
WHAT A DEPLOYMENT EVALUATION COVERS
Make the control model
explicit before making claims.
These are evaluation areas, not blanket guarantees. The current technical model determines what is actually supported and what belongs to another engagement.
Organizational messaging context
How conversations, teams or rooms should be structured around the organization’s work.
Files and shared context
How file exchange and communication context need to relate without exposing private organizational data in public proof.
Administration & access
Which administrative and access boundaries are required and which are supported by the validated technical model.
Deployment & control model
Where infrastructure responsibility sits, what must remain under organizational control and what constraints follow.
SECURITY & PRIVACY BOUNDARY
Control is an engineering property.
Not a badge.
Security depends on architecture, configuration, operation and scope. The page therefore avoids absolute privacy, encryption, zero-access, jurisdiction or compliance promises that have not been technically frozen.
- Threat and control assumptions must be explicit.
- Sensitive topology, credentials and real private communication stay out of public evidence.
- Deployment claims are made only at the level the current technical model supports.
TECHNOLOGY DISCLOSURE
Make the technology visible
where control depends on it.
Underlying technology is not hidden to manufacture value, and it is not foregrounded merely to sound technical. We disclose it when it materially helps evaluation, interoperability, administration, licensing or trust.
Versions, topology and sensitive configuration remain controlled technical detail when public exposure adds risk or no buyer value.
PRODUCT OR ENGAGEMENT?
Choose the route by
the actual control problem.
Controlled organizational communication.
The verified product model fits the communication and operating requirements.
Discuss deployment ↗Broader architecture, review or hardening.
The main problem is security scope rather than the communication product itself.
Explore Cybersecurity ↗A materially bespoke organizational system.
The operating model requires purpose-built architecture beyond product fit.
Explore Custom Software ↗The technical model is still unclear.
Start from requirements and validate the boundary without promising deployment or demo.
Start discovery ↗SAFE PRODUCT EVIDENCE
Evaluate the system
without exposing real conversations.
Product evaluation can use synthetic users, messages and organizational scenarios so the operating model can be understood without turning real conversations, identities, credentials or private files into sales material.
Synthetic organization and users.Safe logical diagrams.Controlled technical detail when needed.
SYNCPAD QUESTIONS
Keep the evaluation
specific and bounded.
Is SyncPad presented as a guaranteed secure or private solution?+
No absolute guarantee is made. Security and privacy depend on the validated architecture, configuration, operation and deployment scope.
Why does the page not lead with protocol or vendor names?+
Technology is disclosed when it materially helps interoperability, administration, licensing or trust. The buyer problem and control model come first.
Is a public demo available?+
This page does not promise one. Evaluation begins with the organization, control requirement and technical environment; a safe demonstration is used only when it is current and appropriate.
When should we use Cybersecurity or Custom Software instead?+
Broader architecture, review or hardening belongs to Cybersecurity. A materially bespoke organizational communication system belongs to Custom Software.
START WITH THE CONTROL REQUIREMENT
Tell us what the organization
needs to control.
We will evaluate the communication context, technical boundaries and whether SyncPad is the right Product path.